Agency Insights & Engineering

The Studio Journal.

Architectural notes, design system breakdowns, zero-latency rendering strategies, and creative philosophy.

Security • Jun 25, 2026

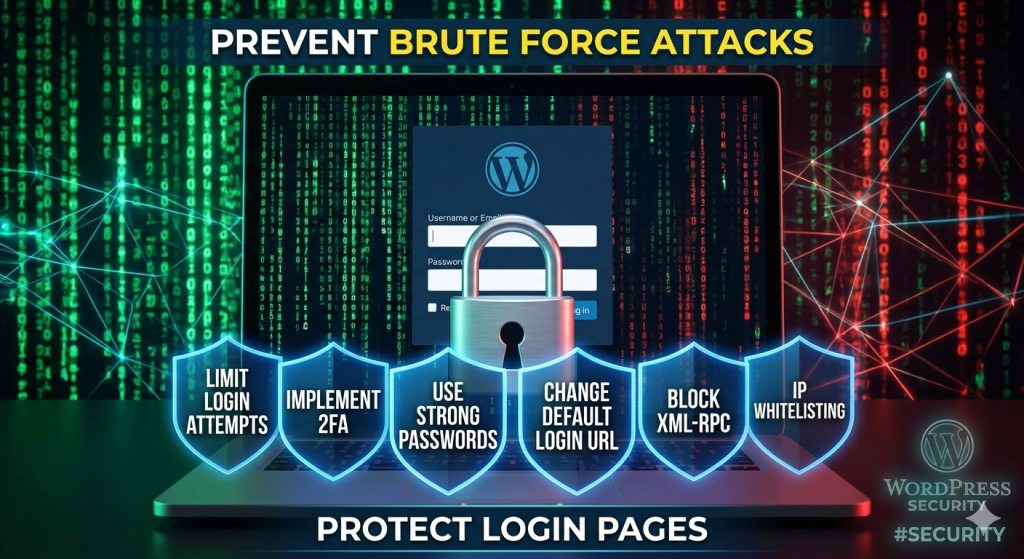
5 Proven Methods to Stop WordPress Brute Force Attacks

Brute force attacks are among the most common threats targeting WordPress websites. In these attacks, automated bots repeatedly attempt different username and password combinations until they gain unauthorized access. Implementing multiple layers of security significantly reduces the likelihood of a successful attack.  1. Limit Login Attempts By default, WordPress allows unlimited login attempts, making it […]
API • Jun 24, 2026

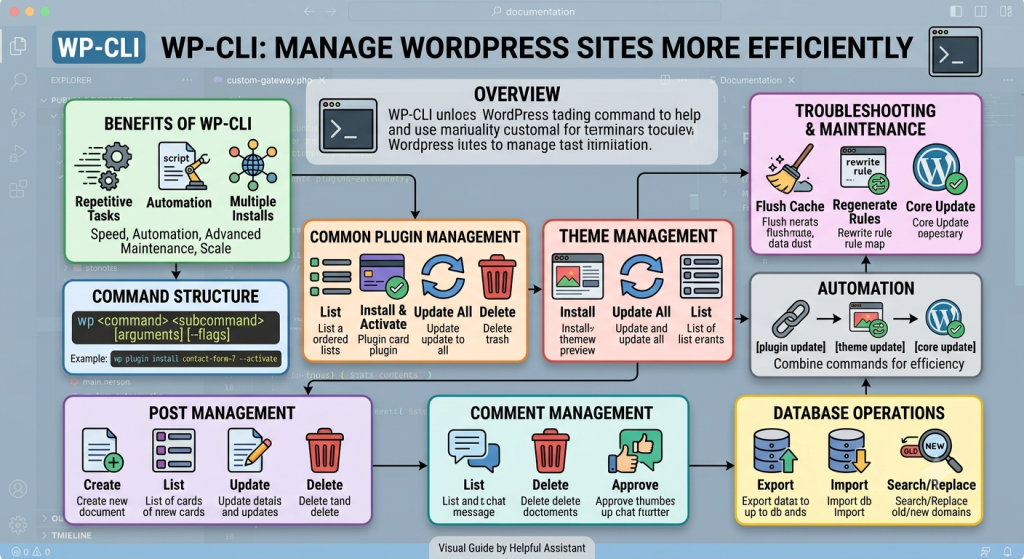
 How to Use WP-CLI to Manage WordPress Sites More Efficiently

WP-CLI (WordPress Command Line Interface) is a tool that allows WordPress administrators and developers to manage WordPress websites directly from the command line. Instead of performing tasks through the WordPress dashboard, users can execute commands in a terminal to manage content, plugins, themes, databases, and site maintenance more efficiently.  Benefits of WP-CLI * Faster execution […]

API • Jun 23, 2026

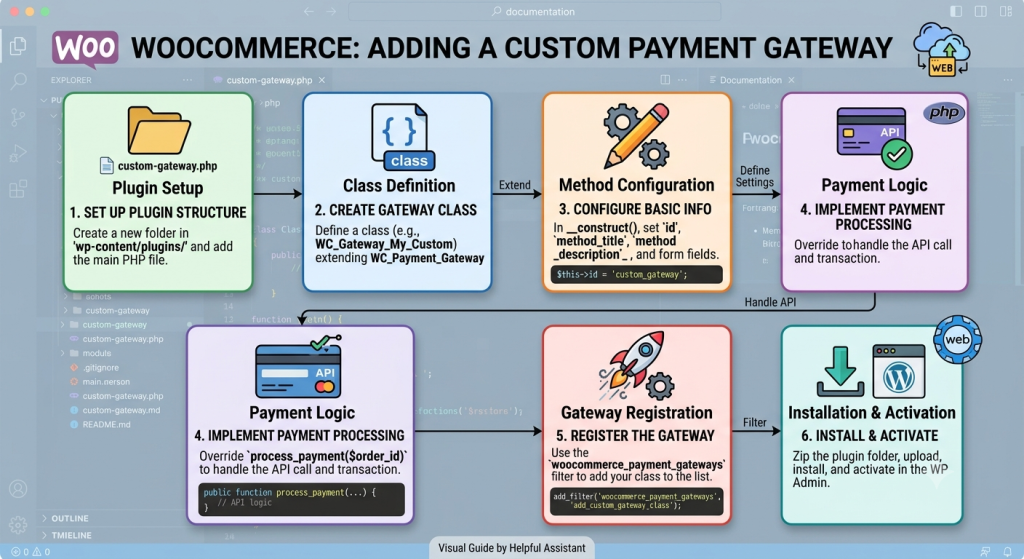
 WooCommerce Payment Gateway API Overview

The WooCommerce Payment Gateway API enables developers to create custom payment gateways that integrate directly with WooCommerce stores. Payment gateways can support online card payments, redirects to external payment providers, embedded payment forms, or offline payment methods.  Gateway Types WooCommerce supports several gateway implementations: 1. **Form-Based Gateways** – Redirect customers to a third-party payment page. […]

WooCommerce • Jun 21, 2026

 Best WordPress Hosting Providers: A Practical Guide

Choosing the right WordPress hosting provider is one of the most important decisions for website performance, security, and long-term growth. A good hosting service should offer fast loading speeds, strong uptime, reliable customer support, security features, and scalability.  Key Factors to Consider  Performance * Fast server response times * SSD or NVMe storage * Built-in […]

Security • Jun 21, 2026

 How to Fix a 500 Internal Server Error in WordPress

A 500 Internal Server Error is a generic server-side error that indicates something has gone wrong on the website, but the server cannot identify the exact cause in the browser output. Common causes include plugin conflicts, theme issues, corrupted configuration files, PHP memory limits, or server misconfigurations.  Step 1: Check Error Logs Enable WordPress debugging […]

API • Jun 20, 2026

 Securing the WordPress REST API 

 1. Overview The discussion focuses on whether the WordPress REST API should be disabled or restricted for security reasons, and what the real risks actually are.  2. Key Conclusion The REST API is **not inherently insecure**. It is a core WordPress component and is widely used by: * The block (Gutenberg) editor * Themes and […]

CPT • Jun 20, 2026

 Creating a WordPress Custom Post Type

A Custom Post Type (CPT) in WordPress allows developers to create specialized content types beyond the default Posts and Pages. Examples include Books, Movies, Products, Events, and Pets. Using a CPT helps organize content and provides a dedicated administration interface within the WordPress dashboard.  Why Use a Custom Post Type? WordPress includes several built-in post […]

WooCommerce • Jun 19, 2026

Optimizing a WordPress/WooCommerce Store to Load in Less Than 3 Seconds

Fast-loading e-commerce websites improve user experience, conversion rates, and search engine rankings. This document outlines the key techniques used to optimize a WordPress/WooCommerce store to achieve page load times below three seconds.  1. Infrastructure and Hosting Performance begins with the hosting environment.  Recommendations * Use reliable cloud hosting with sufficient CPU and memory resources. * […]

Security • Jun 19, 2026

 How to Protect Against SQL Injection Attacks

SQL Injection (SQLi) is a web application vulnerability that occurs when user-supplied input is improperly incorporated into SQL queries. Attackers can exploit this weakness to access, modify, or delete data stored in a database, potentially compromising sensitive information and system integrity.  Risks of SQL Injection Successful SQL injection attacks may allow an attacker to:  Recommended […]